This is my little corner of the internet. I’ll be documenting my journey into cybersecurity; the things I learn, the stuff I break, and the rabbit holes I inevitably fall into. Still learning. Still experimenting. Still breaking things. Hopefully fixing most of them.
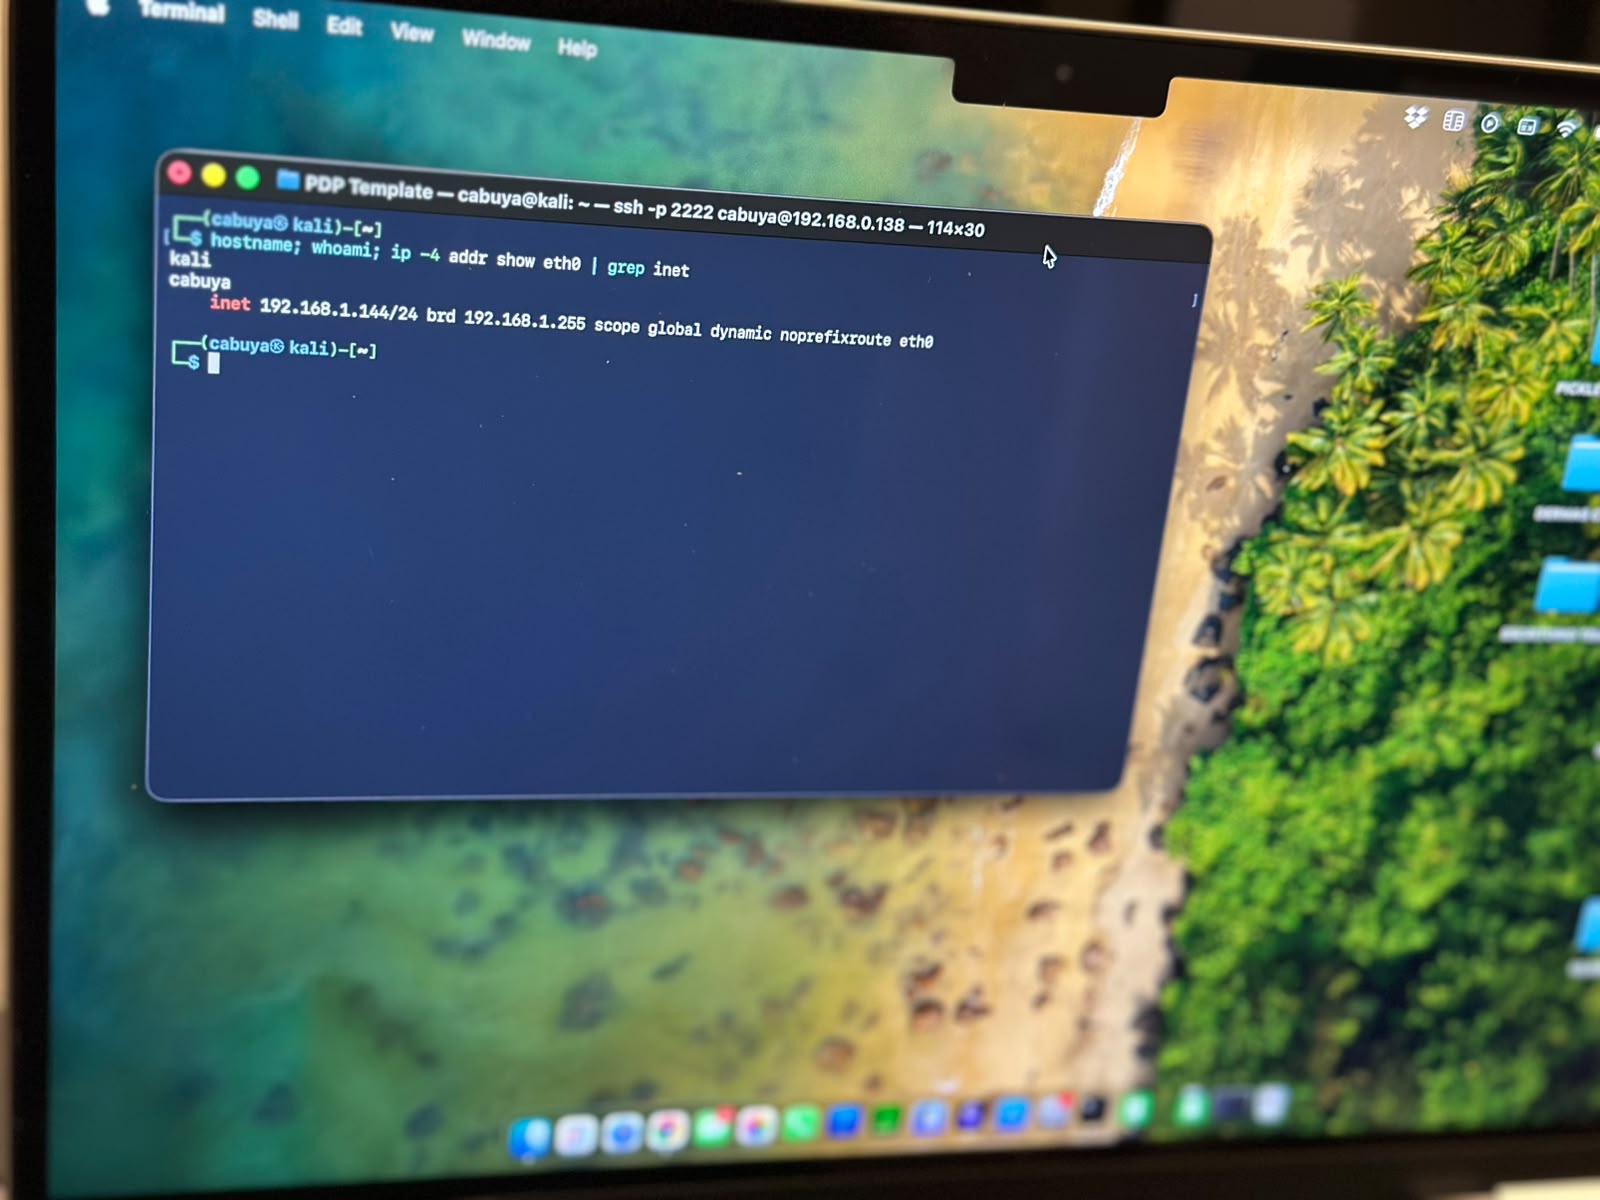
Reaching My Kali Box Through a Second Router: SSH Across Double NAT, Then Into Hack The Box
I keep my Kali Linux machine tucked away on its own little subnet, wired into a second router that itself hangs off the main house network. That isolation is on purpose: the lab stays separate from the phones, TVs and everyone else’s traffic. But it raises an obvious question: If the Kali box is behind its own router, can I still reach it from my MacBook on the main Wi-Fi, SSH straight in, and from there launch a Hack The Box session without ever touching the machine physically? ...
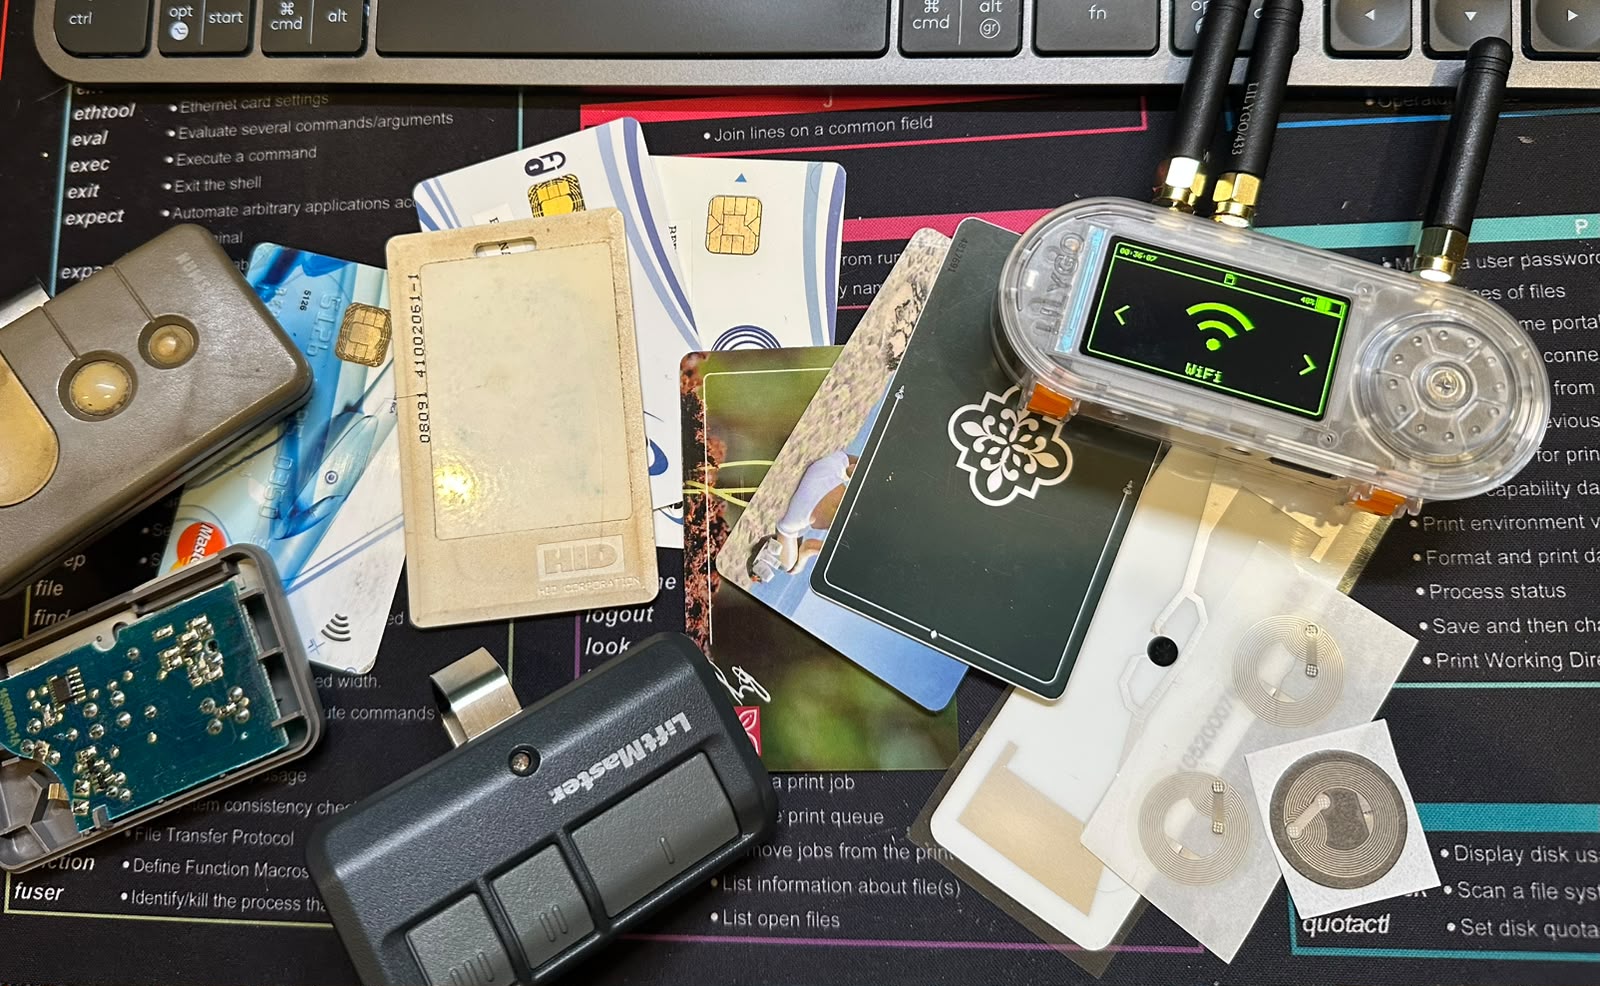
One Gadget, Three Radios: First Tests With the T-Embed CC1101 Plus
I bought a new toy: a LilyGO T-Embed CC1101 Plus. It’s a pocket-sized, battery-powered multi-radio tool in a clear case, with a little scroll wheel and three antennas. Think of it as a Swiss Army knife for the airwaves: sub-GHz radio, Wi-Fi, Bluetooth and NFC/RFID in one device you can drive with your thumb. I didn’t buy it just to collect gadgets. Three capabilities sold me on it: ...
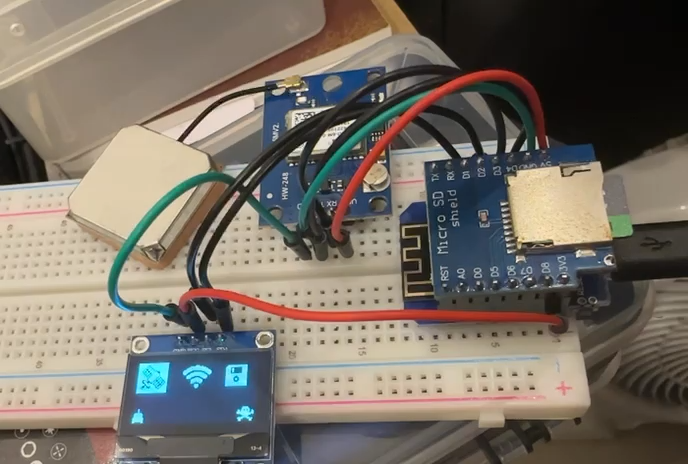
Finishing What I Started: Building an ESP8266 Wardriver a Year After PWNED 0x08
Last year I attended PWNED 0x08, a cybersecurity conference here in Costa Rica, and signed up for the workshop “RF Exploration: Introduction to Sniffing with ESP32/ESP8266.” The goal was simple and very fun: build a pocket-sized wardriver, a device that listens for Wi-Fi networks around you, tags each one with a GPS position, logs everything to an SD card and shows its status on a small screen. I walked out of that workshop with a bag of parts and a project I hadn’t finished. ...